JIT MICROLESSONS / GUIDANCE IN CONTEXT
Security Guidance.
When Developers
Need It.
Focused application security guidance for the moment a developer is working on a vulnerability.
CWE-MAPPED GUIDANCELANGUAGE-SPECIFIC MATERIALSUBSCRIPTION ACCESS
Same Finding.
Relevant Guidance.
Use the vulnerability class to connect a finding with learning that supports the developer’s next step.
ILLUSTRATIVE TICKET / NOT A LIVE INTEGRATION
Cross-Site Scripting
Include focused educational guidance alongside the security finding and remediation work.
VULNERABILITY MAPPING CWE-79
RELATED LEARNINGPreventing Cross-Site Scripting in JavaScript
Lesson links can be placed in tickets or security-results platforms. 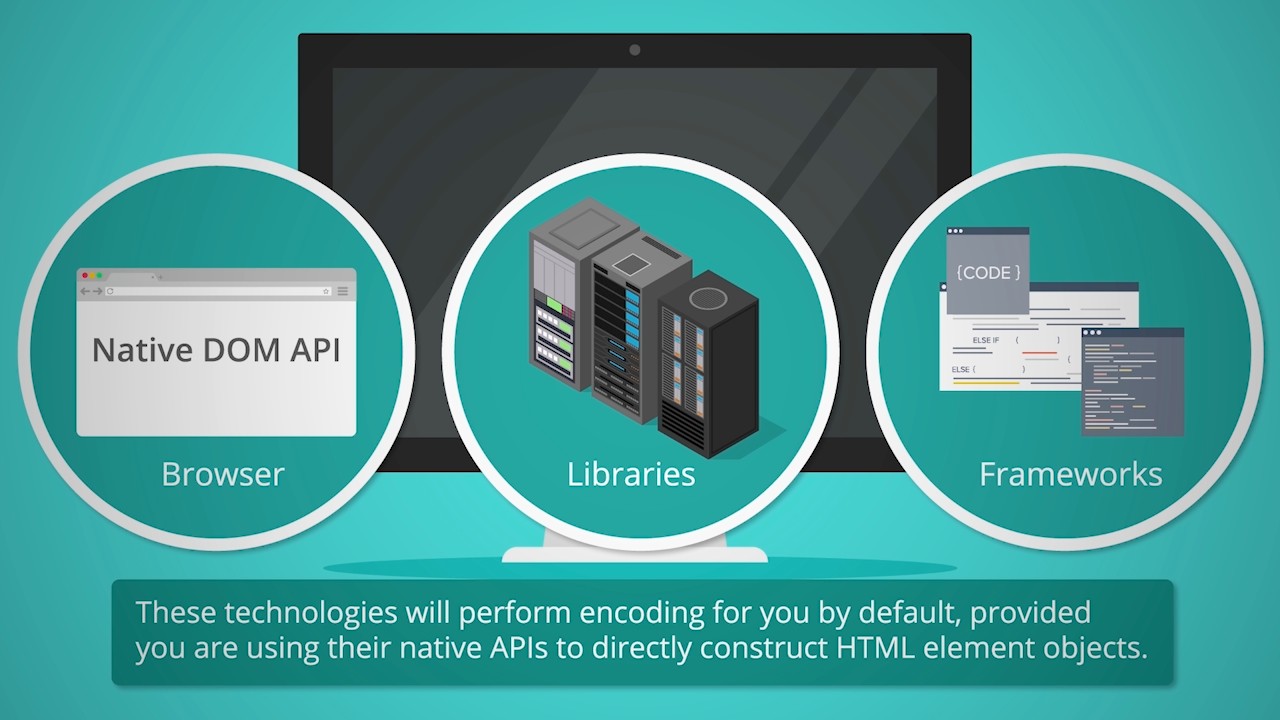
FROM THE PUBLISHED REFERENCE MATERIAL
See the Guidance.
Preventing Cross-Site Scripting in JavaScript. Actual video still; select a finding to see its matching material.
SELECTED LESSONCross-Site Scripting / JavaScript
FOCUSED ON THE VULNERABILITY
Understand the Risk.
Support the Repair.
The reference library includes vulnerability overviews, language-specific exploitation and prevention material, and supporting PDF guidance.
ASK ABOUT YOUR COVERAGE ↗Cross-Site Scripting
SQL & NoSQL Injection
OS & HTTP Header Injection
Directory Traversal
XML External Entities
Insecure Deserialization
Cross-Site Request Forgery
Insecure JWT Use
Components with Known Vulnerabilities
And more vulnerability classes
Guidance for the Technologies Your Team Uses.
.NETJavaJavaScriptPythonRubyGo
Bring the Learning
Into the Workflow.
Discuss the mapping, link placement, and access model that fit your environment.
Ticketing Systems
Append relevant microLesson links to vulnerability tickets using CWE mappings.
02Security-Results Platforms
Place targeted learning where teams review security findings and plan remediation.
03Your Own Software
Explore embedding microLesson links in your proprietary software and workflows.
REINFORCE WHAT TEAMS LEARN
Learning That Meets
the Work in Front of You.
Tell us about your languages, vulnerability classes, and existing tools. We’ll discuss subscription access and the right approach for your team.