01 / FOUNDATION
ELEARNING / PRACTITIONER-WRITTEN SECURITY TRAINING
Security Learning.
Built Around
Your People.
From everyday security decisions to building secure software, develop practical capability around the responsibilities of each role.
WRITTEN BY SECURITY PRACTITIONERS WHO BUILD SOFTWARE20+ YEARS OF DEVELOPMENT & SECURITY EXPERIENCE
A Shared Foundation.
A Relevant Next Step.
Choose a role to see the three-stage approach: build awareness, apply security to day-to-day responsibilities, then advance into relevant risks.
Secure EmployeeSecure ITSecure ManagerSecure DeveloperSecure ProductSecure ArchitectSecure PlatformSecurity Team
Secure Developer
02 / RESPONSIBILITIES
Apply by Role
03 / RELEVANT RISKS
Advance by Risk
General Security Awareness is included across the roles. The next steps reflect the work each role does and the risks it influences.
PLAN TRAINING FOR YOUR TEAM ↗New & Updated.
Course Highlights.
Explore the latest additions and updates to our security training.
RECENTLY UPDATED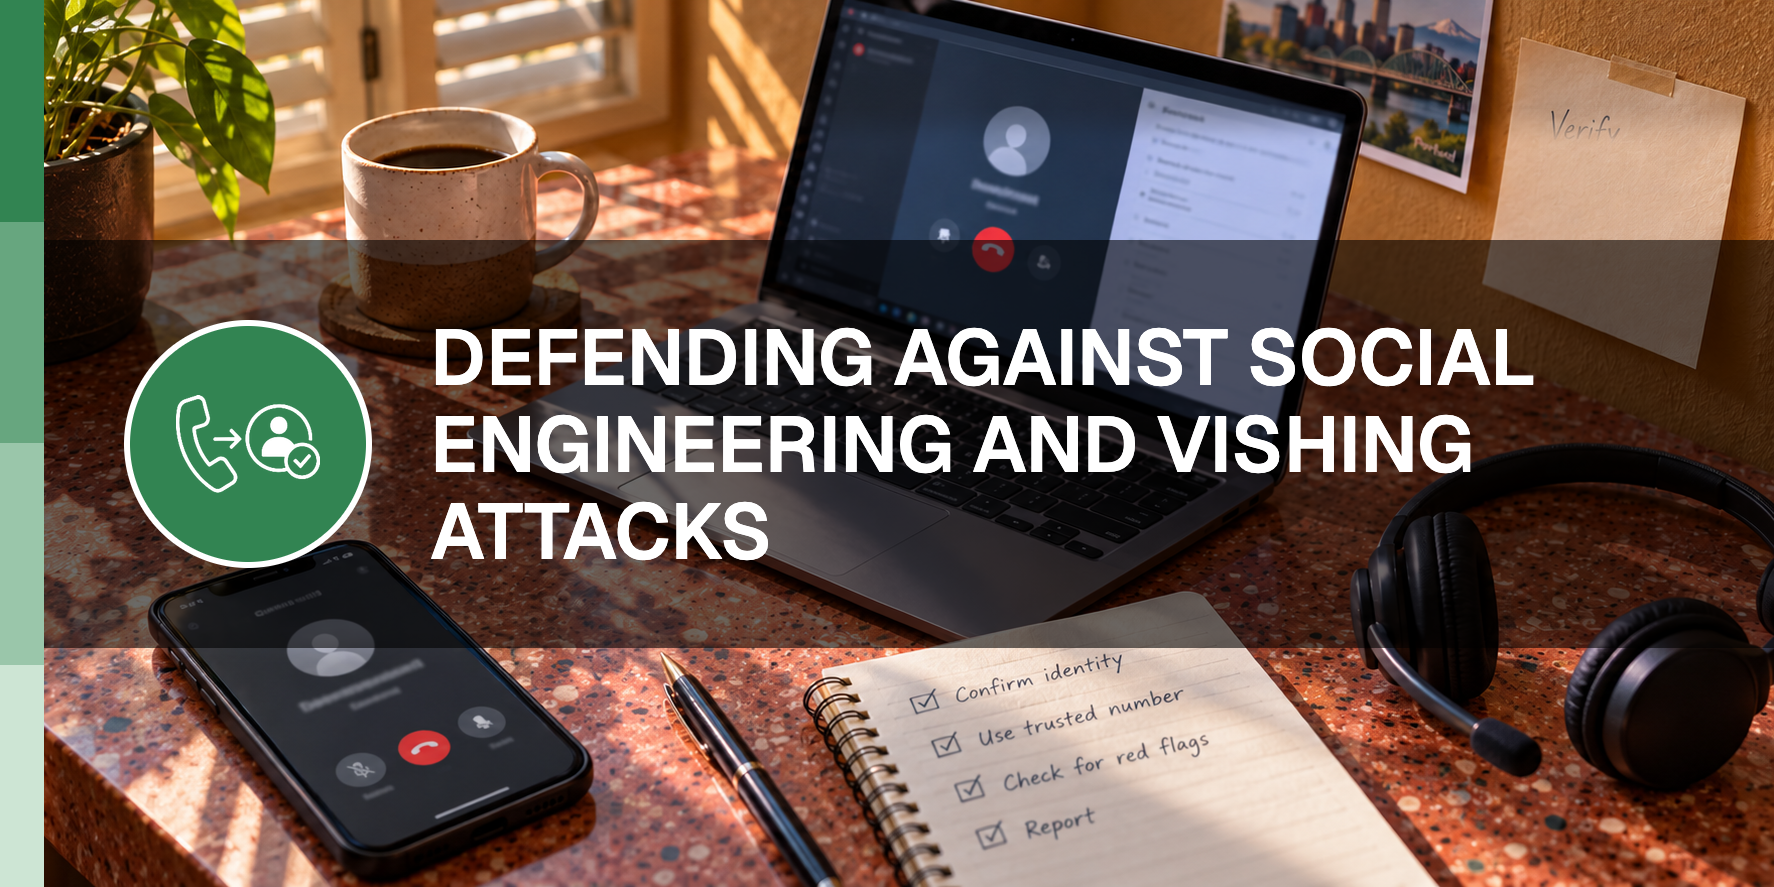
GENERAL SECURITY AWARENESS
Defending Against
Social Engineering and Vishing Attacks.
Recognize social engineering tactics and practice responding to suspicious calls.
Phishing & social engineering · Authentication · Data handling · Remote work · Safe GenAI use
NEW COURSE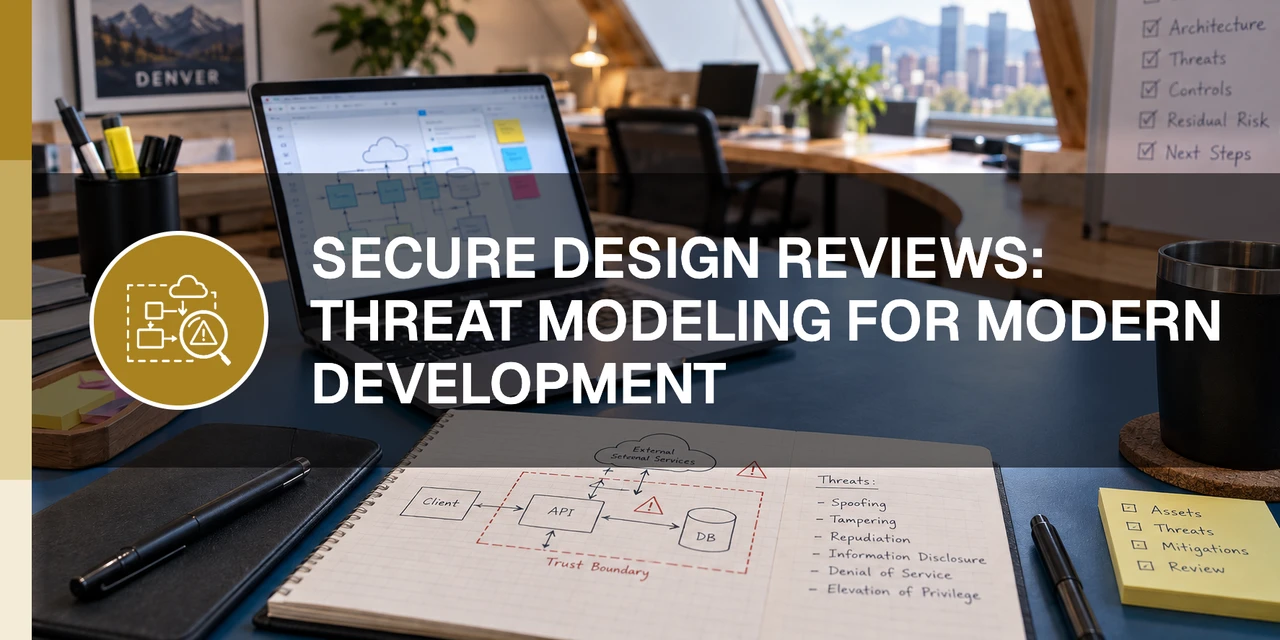
APPLICATION SECURITY
Secure Design Reviews:
Practical Threat Modeling.
Explore practical threat modeling to identify risks early in software design.
Secure coding · APIs · Threat modeling · Secure SDLC · Cloud & containers · GenAI application security
ELEARNING / COURSE PREVIEWS
See the skills.
Explore the learning.
See how Infrared courses explain real security challenges and connect them to the work people do.
 Think before You Click
GENERAL SECURITY AWARENESS
Think before You Click
 API Security
APPLICATION SECURITY
API Security
 GenAI Safe Use
GENERAL SECURITY AWARENESS
GenAI Safe Use
 Application Security Essentials
APPLICATION SECURITY
Application Security Essentials
 Container Security
APPLICATION SECURITY
Container Security
 Security Compliance for Developers
APPLICATION SECURITY
Security Compliance for Developers
 GenAI Security
APPLICATION SECURITY
GenAI Security
 Secure Coding in Java
APPLICATION SECURITY
Secure Coding in Java
 Secure Design & Threat Modeling
APPLICATION SECURITY
Secure Design & Threat Modeling
 Security Throughout the SDLC
APPLICATION SECURITY
Security Throughout the SDLC
BUILD YOUR PROGRAM
Learn the Concepts.
Put Them to Work.
Combine a structured learning foundation with practical experiences and focused reinforcement.
Courses & Learning Paths
Establish foundational knowledge, then select courses suited to responsibilities, technology, and risk. SCORM-compliant content supports delivery through existing learning environments.
Practical microLabs
Practice decisions and technical skills through General Security Awareness and Application Security activities, within courses or as standalone learning.
JIT microLessons
Reinforce application security concepts with three-minute, CWE-mapped guidance alongside vulnerability findings and remediation work.
YOUR PEOPLE. YOUR PRIORITIES.
Build a Program
That Fits Your Team.
Explore the courses already available, or talk with us about a role-based training approach.